iPhone App Steals USDT Worth IDR 9 Billion, Here's How It Attacks
2026-09-23
A crypto whale tracker app called FomoPeek managed to bypass the App Store security system and steal nearly IDR 9 billion, equivalent to $580,000 in USDT, from its users.
Security firm SlowMist revealed that this iPhone app breached the iOS sandbox and accessed the device's Keychain, paving the way for attackers to steal crypto wallet private keys without victims ever connecting their wallets to the app.
This incident is a stark reminder that crypto wallet security on iPhone cannot rely solely on official status from the App Store.
Key Takeaways
- FomoPeek, a crypto whale tracker app on the App Store, contains malware that breaches the iOS sandbox and steals $580,000 USDT, around IDR 9 billion.
- The malicious code was in versions 1.1 and 1.2, released on September 9 and 12, 2026, then cleaned in version 1.3 on September 17, 2026.
- Victims did not need to connect their wallet to this app because the malware directly accessed the iOS Keychain and stealthily stole private keys or seed phrases.
What Is FomoPeek and How Does Its Attack Work?
FomoPeek was marketed as a read-only tool for monitoring large whale transactions on Ethereum, Solana, and Tron. However, SlowMist, working with the OKX security team, found two hidden modules unrelated to the app's official function, as reported by CryptoSlate.
One module communicates with an external command-and-control server. The other module contains a kernel exploitation framework with eight different attack methods that automatically adapt to the victim's iPhone model and iOS version.
SlowMist founder Yu Xian explained that once the attack succeeds, the app can read and decrypt the system Keychain and access other apps' files on the same device.
If you want to store crypto assets with greater peace of mind, start trading and keep funds through an official OJK-licensed platform like Bittime while still maintaining the security of your personal wallet.
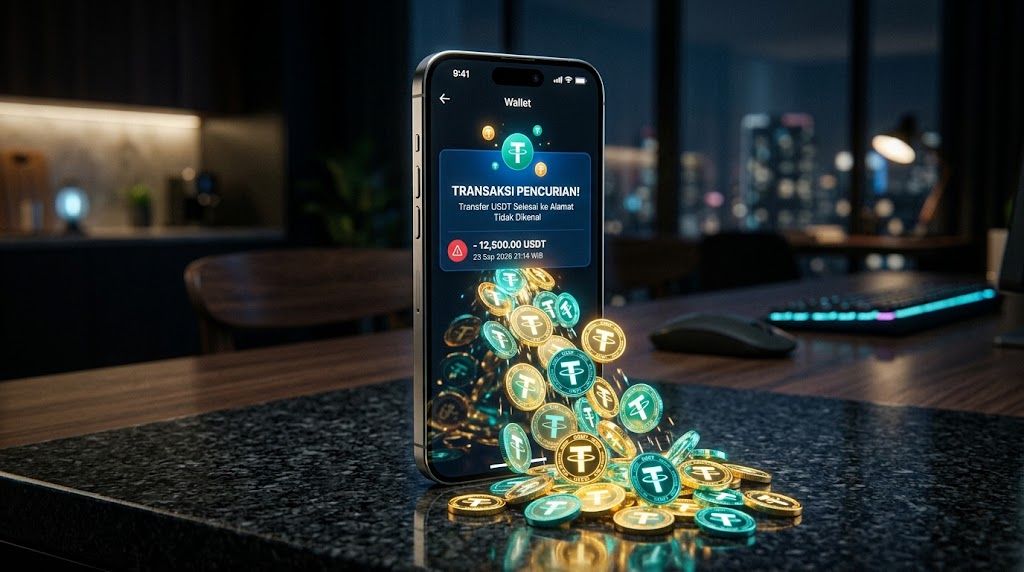
Eight Exploit Methods That Breach the iOS Sandbox
FomoPeek's exploitation framework targets a very wide range of iOS versions, from iOS 12.0 to 18.7, as well as iOS 26.0 and 26.1, according to a Crypto Briefing report. This means nearly every iPhone generation still actively in use could be affected.
More concerning, this attack function was already running automatically at intervals during the investigation, indicating exploitation was still ongoing when this case was uncovered.
Once it successfully breaches the sandbox, the malware can access private keys, seed phrases, login credentials, chat history, and even other files belonging to different apps on the same iPhone.
Read Also: Purbaya Removed from Finance Ministry, Becomes BI Governor? Check the Facts
Where Did This Stolen IDR 9 Billion Flow?
Blockchain analysis firm Salus tracked the flow of stolen funds from the attacker's address. Around 401,028 USDT was routed through three intermediary addresses to the FixedFloat exchange. Another 20,000 USDT moved through two deposit addresses before being consolidated into a KuCoin hot wallet.
In addition, 111,458 USDT was recorded flowing to an address linked to an escrow platform, while 10,000 USDT passed through the CCE mixing service. Salus also suspects this group is connected to a separate private key theft case in June 2026, although the exact technique is still being verified.
Read Also: BIS Reveals New Potential for XRP Ledger for Digital Financial Systems
How to Protect Crypto Wallets on iPhone from Similar Malware
Binance, OKX, Gate, Bitget Wallet, and Rabby collectively issued similar advisories after this incident. Users were asked to immediately delete FomoPeek, update iOS to the latest version, and move funds to a new wallet created on a clean device.
Deleting the app or updating the system alone cannot revoke a private key that the attacker has already copied, so migrating to a new wallet is a mandatory step.
Some additional steps crypto investors can take: avoid storing seed phrases digitally on the same device as an active wallet, use a hardware wallet for large amounts of funds, and always check the developer's reputation before installing crypto-related apps, even if the app is on the official App Store.
Read Also: Popular Tokenized Stocks in 2026: Tech Stocks Become Investor Favorites
Conclusion
The FomoPeek case proves that official App Store status does not automatically guarantee the full security of a crypto app.
With losses reaching $580,000 USDT and exploitation targeting almost all iOS versions, this incident is an important reminder for anyone managing a crypto wallet on iPhone to be more selective in choosing apps and to separate the storage of large assets from devices used daily.
Check the prices of Bitcoin (BTC), Ethereum (ETH), XRP, Solana (SOL), GRAM, and BNB as well as leading memecoin DOGE. You can trade directly on Bittime!
Bittime is a licensed Digital Financial Asset Trader (PAKD) platform supervised by the Financial Services Authority — where you can buy Bitcoin in Indonesia and hundreds of other crypto assets starting from IDR 10,000. The registration process is fast, secure, and can be started today.
Monitor USDT to IDR conversion and the price movements of your favorite crypto assets in real time. All available in one crypto investment app that can be downloaded for free on the Play Store.
Ready to start? Register now on Bittime and execute your investment strategy with a platform trusted by millions of users in Indonesia.
FAQ
What is FomoPeek?
FomoPeek is an App Store app originally marketed as a tool for monitoring crypto whale transactions on Ethereum, Solana, and Tron. Versions 1.1 and 1.2 of this app were found to contain malware that stole users' wallet data.
How does FomoPeek malware steal crypto?
The malware breaches the iOS sandbox and then accesses the system Keychain to steal private keys, seed phrases, and login credentials, without the victim needing to connect a wallet to the app. The attack automatically adjusts its method based on the victim's iPhone model and iOS version.
Are official App Store apps always safe?
Not always. The FomoPeek case shows that an app that passes App Store review can still insert malicious code in a subsequent update.
What should you do if you ever installed FomoPeek?
Immediately delete the app, update iOS to the latest version, and move all funds to a new wallet created on a clean device. Do not reuse the old private key or seed phrase because it is at risk of having been leaked.
Disclaimer: The views expressed belong exclusively to the author and do not reflect the views of this platform. This platform and its affiliates disclaim any responsibility for the accuracy or suitability of the information provided. It is for informational purposes only and not intended as financial or investment advice.
.png)