Not Stealing Passwords, This Is How Hackers Allegedly Attacked Polymarket
2026-10-30
Polymarket temporarily suspended trading activities on its international platform after a number of users reported losing assets without making any transactions.
The security incident, which occurred in late October 2026, is believed to be related to a compromise of one of the third-party service providers connected to the platform.
This issue led Polymarket to restrict trading activity during the investigation process.
The company later stated that it had fixed the disruption, restored trading, and would compensate all affected users.
The 2026 Polymarket hack case has once again highlighted the security risks on crypto platforms.
Threats do not always come from hacking the main system or stealing passwords, but can also arise through external services that a platform uses.
Key Takeaways
Polymarket has temporarily suspended international trading after discovering a security incident involving a third-party service provider.
The service provider linked to the incident is DebugBear, a company that provides website performance monitoring services.
Polymarket stated that it has fixed the problem and will compensate all affected traders.
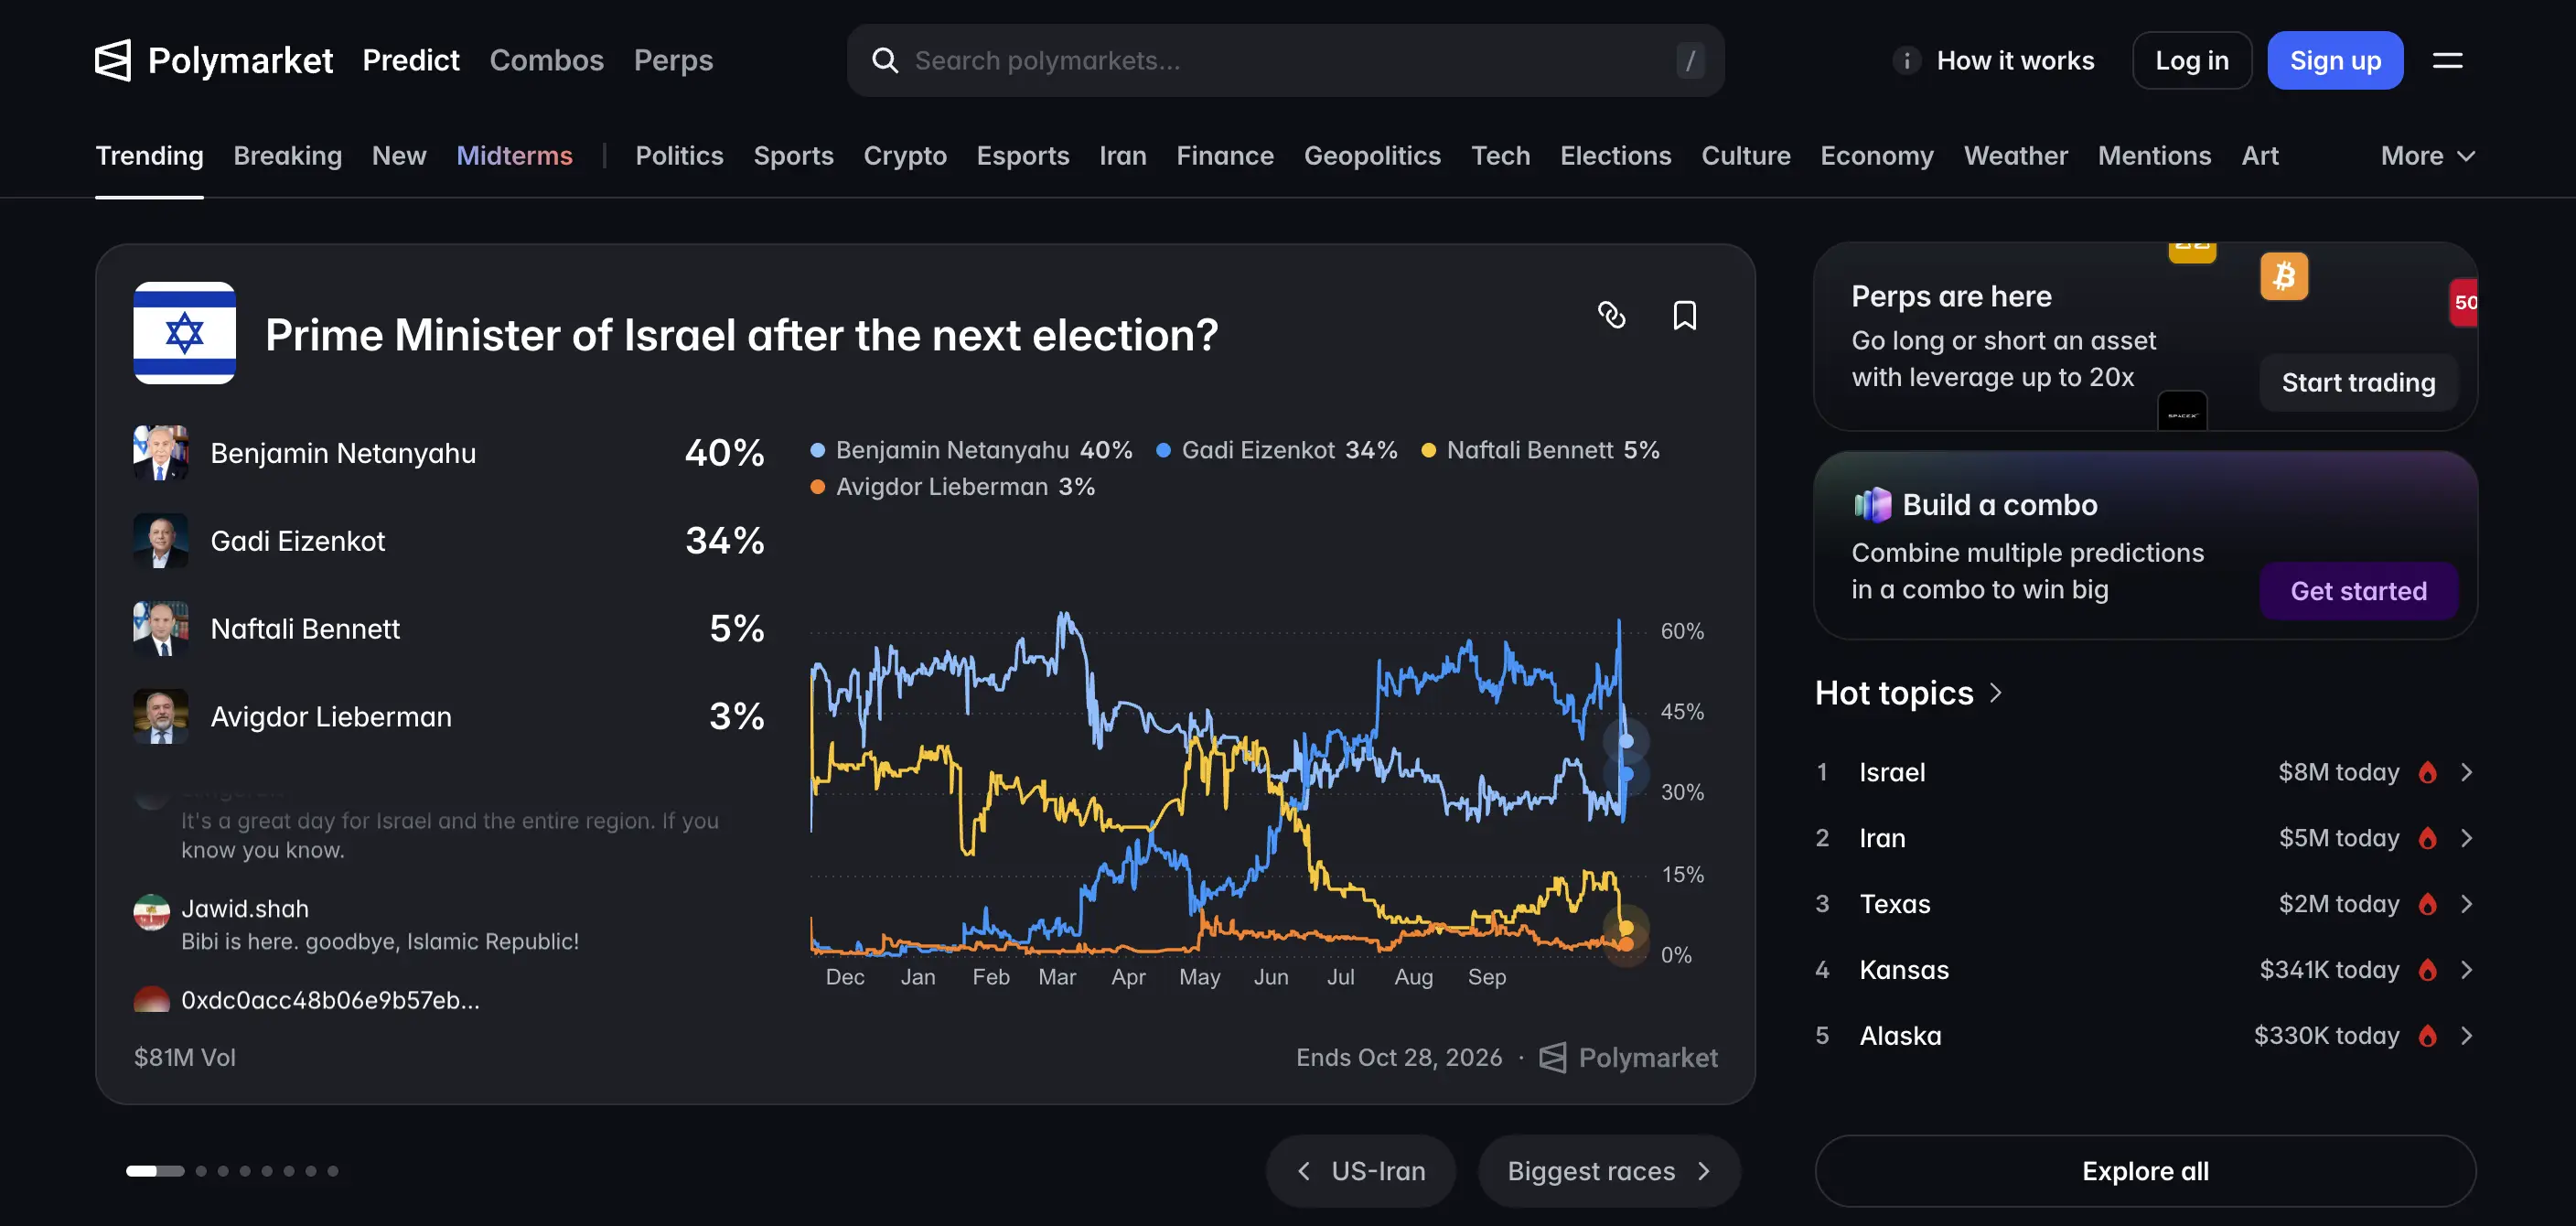
Chronology of Polymarket Trading Halt
Source: polymarket.com
This incident started to attract attention after a number of users reported unusual activity on Polymarket accounts.
Some traders claim to have lost their balances and assets that they previously owned without giving consent for the transaction.
A CoinDesk report on October 29, 2026, stated that several users of the international Polymarket platform experienced unauthorized asset withdrawals.
The company later confirmed a security issue involving one of its third-party service providers.
Read Also: BNB Weakens After Alleged Binance Hack, Panic Selling Depresses Price
Polymarket Restricts Trading Activities
As a precautionary measure, Polymarket first activated cancel-only mode.
In this mode, users can still cancel orders that have already been placed, but cannot enter new trading orders.
Polymarket also temporarily suspended relayer activity during the investigation. This measure was taken to limit transaction activity until the security issue was resolved.
According to the incident history on its official status page, the outage began on October 29, 2026, at 18:05 UTC and was declared resolved at 19:05 UTC.
Thus, the activity stoppage lasted about an hour.
After the issue was fixed, Polymarket announced that trading activity had resumed.
The company also stated that it would compensate all affected users.
Read Also:Alleged Binance Hack: US$5.7 Billion in Crypto Assets Moves into the Spotlight
What Caused the Polymarket Security Breach?
Polymarket confirmed that one of its third-party service providers experienced a security compromise.
However, the company did not disclose all the technical details regarding how the attackers gained access and executed the attack.
The Washington Post report identified DebugBear as the service provider linked to the incident.
DebugBear is a company that provides performance monitoring and user experience services on websites.
Read Also:CoinDCX Hack: 15.99 Million USDT Lost, Initially Called a False Alarm
Alleged Involvement of DebugBear
Website performance monitoring services typically use code or scripts embedded on a site's pages. These scripts help managers understand page load speeds and visitor experience when accessing their services.
Integrations like this can make site management easier, but also pose risks if the external service provider experiences a security compromise.
In the case of Polymarket, DebugBear's involvement was reported by a number of media outlets after the incident occurred.
The Washington Post reported that the company also acknowledged it was facing a security incident and asked customers using its Real User Monitoring (RUM) product to remove the code installed on their sites.
However, it is important to distinguish between confirmed information and technical conjecture.
Polymarket has officially confirmed the compromise of its third-party provider, but has not yet published a full investigative report detailing all stages of the attack.
Read Also:Ledger Hardware Wallet Allegedly Modified, Crypto Users Need to Be Wary
What is a Third-Party Provider Hack?
A third-party provider hack is an attack that exploits weaknesses or compromises in external service providers connected to a company.
Attackers do not have to directly compromise the platform's core systems.
They may try to exploit support services that have integration with the company's systems.
In a digital ecosystem, external services can include analytics tools, performance monitoring, payment systems, and marketing tools.
If one of these services is compromised, the impact could potentially reach the companies that use it.
That is why platform security is not enough to rely solely on protecting internal infrastructure.
Third party oversight is also an important part of risk management.
Are User Funds Stolen Without Password and Seed Phrase?
One of the things that made this case interesting was the reports of user assets being transferred without any passwords or seed phrases being handed over to the attackers.
A technical report cited by Decrypt mentions the alleged use of malicious scripts to exploit active user sessions.
The script is alleged to be able to interact with Polymarket's trading functionality to execute transactions without the account owner's consent.
However, this mechanism is the result of a security researcher's analysis reported in the media, not the full technical explanation that Polymarket has published.
Understanding the Risks of Session Hijacking
Session hijacking is a type of attack where an unauthorized party takes over or abuses a user's authentication session.
When a user successfully logs in to a platform, the system usually maintains a session so that the user does not need to enter a password every time they open a page or perform certain activities.
If the session is successfully abused, an attacker could potentially perform certain actions through authenticated access.
The differences between several types of attacks on digital accounts can be seen below:
The Polymarket case shows that keeping passwords and seed phrases secret is important, but not enough to eliminate all digital security risks.
Crypto trading is more convenient when asset security and withdrawal processes are reliable, register at Bittime and start trading more safely and calmly!
How Much Did Users Lose Due to the Polymarket Hack 2026?
As of the publication of the incident report, Polymarket has not yet announced the details of the number of users affected or the total assets lost.
CoinDesk cited DeFiLlama data that estimated losses in the incident at around US$2.7 million.
This figure comes from third-party tracking and is not the official loss amount announced by Polymarket.
The Washington Post also reported that users complained of losing funds after the security incident came to light.
However, the full scope of the impact on users cannot be ascertained from the available information.
Want to have exposure to American stocks? Register at Bittime and start investing through tokenized stocks.
Polymarket Promises Reimbursement
In its official announcement, Polymarket stated that all affected users will receive compensation.
The company also stated that the incident has been reported to UK law enforcement. This action is related to an investigation into the compromise of a third-party service provider.
However, Polymarket has not yet fully explained the reimbursement mechanism, payment schedule, or verification process for users who submit claims.
Users who feel affected should follow official announcements and check their account activity history.
Read Also:The Impact of the AI Bubble on Crypto: Can Bitcoin Survive?
What Impact Does This Incident Have on Crypto Platform Security?
The Polymarket incident serves as a reminder that security risks can arise from the various components that support a platform's operations.
Using third-party services can indeed help improve efficiency and user experience.
However, such integration can also expand the attack surface if the service provider does not have adequate security in place.
Preventive Measures for Users
Crypto platform users can take several steps to reduce risks, including:
Check transaction history and account activity regularly.
Avoid links or sites that cannot be verified.
Use additional authentication if available.
Revoking unknown sessions or connections.
Contact official support services when you find suspicious transactions.
On the other hand, platform managers need to conduct audits of external services, limit access granted to third-party providers, and monitor the integrity of the code integrated with the site.
This case also shows the importance of transparency when an incident occurs.
Information about the causes, scope of impact, and recovery process can help users understand the risks and determine what steps need to be taken.
For users who want to start trading digital assets, it is important to learn about the platform's security systems, terms of service, and risks before making a transaction.
Register at Bittime can be an option for learning about crypto asset trading while still paying attention to account security and investment risks.
Bittime is a licensed and regulated Digital Financial Asset Trader (PAKD) supervised by Indonesia’s Financial Services Authority (OJK) — where you can buy Bitcoin in Indonesia and hundreds of other crypto assets starting from just Rp10,000. The registration process is fast, secure, and you can get started today.
Track USDT to IDR conversions and monitor your favorite crypto assets in real time. Everything is available in one crypto investment app that you can download for free on the Play Store
Ready to start? Register now on Bittime and execute your investment strategy with a platform trusted by millions of users in Indonesia.
FAQ
Why did Polymarket stop trading in October 2026?
Polymarket has temporarily suspended international trading after discovering a security incident involving one of its third-party service providers. The suspension is a precautionary measure while the investigation and remediation process continues.
What caused the Polymarket hack in 2026?
Polymarket confirmed that one of its third-party service providers experienced a security compromise. Media reports linked the provider to DebugBear, a website performance monitoring company.
Do users lose funds without providing passwords and seed phrases?
Several users reported losing assets without directly making transactions. Technical analysis reported in the media suggests the misuse of active user sessions, but Polymarket has not yet released a full technical explanation.
Will Polymarket replace lost user funds?
Yes. Polymarket stated that it will compensate all affected users. However, the details of the reimbursement mechanism and timeline have not been fully disclosed.
Is Polymarket trading back to normal?
Yes. According to the official status page, the incident has been resolved, and trading activity resumed after a temporary suspension of approximately one hour.
Disclaimer: The views expressed belong exclusively to the author and do not reflect the views of this platform. This platform and its affiliates disclaim any responsibility for the accuracy or suitability of the information provided. It is for informational purposes only and not intended as financial or investment advice.
.png)