ARTEX AI Becomes a Hacker Weapon, Crypto Companies Also at Risk
2026-11-18
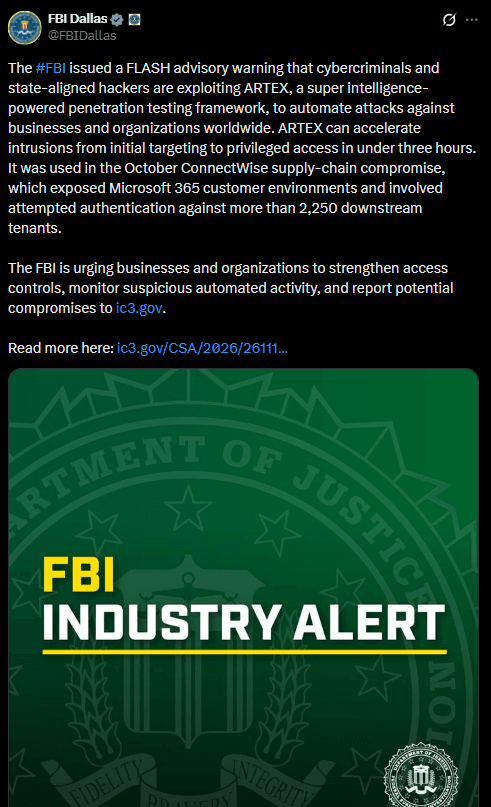
Less than three hours. That is the fastest time recorded by the FBI for an AI cyberattack, from initial targeting to privileged access on the victim's network. The tool used is called ARTEX AI, an AI-agent-based penetration testing framework that is now being misused.
In the FBI cybersecurity warning on November 13, 2026, hackers using this AI were said to target various sectors. In one incident whose pattern matched ARTEX, the attacker even searched for Ethereum keystore files on the victim's server, so crypto exchanges are also on alert.
Key Takeaways
- ARTEX AI enables AI agents to carry out staged hacking automatically, with some intrusions reaching privileged access in less than three hours, according to the FBI.
- Amazon recorded attempts to breach identity verification at two crypto exchanges via deepfake, but the vendor rejected all recorded attempts.
- The exploited gaps are classic, such as default credentials and leaked keys, so credential hygiene becomes the main defense.
What Is the ARTEX AI Framework and Why the FBI Spoke Out
ARTEX works like an automated team of hackers. An operator states the goal in everyday language, then a planning agent divides tasks among worker agents that use common hacking tools such as Nmap and curl. A large language model determines the next step, according to Amazon Threat Intelligence as cited by BigGo Finance.
This framework, created by a Chinese developer, was originally open-source. Its source code was closed on October 8, 2026, according to SentinelOne, but forks and repository copies are still circulating, including ARTEX PRO. Censys counted 1,465 exposed ARTEX consoles as of November 4.
The FBI warning dated November 13 summarizes 11 previous reports. One example is the breach of a South Korean financial institution in August, with data on about 67,000 people stolen. The cost is also low. SentinelOne cites Check Point research that one campaign spent about US$ 145 to US$ 1,500 on AI models.
Attacks like this make platform choice important. If you want to start trading on a platform that is registered and supervised by OJK, register at Bittime and review its security standards in the following section.
Read Also: FBI Asks Police to Investigate Megaspeed, Where Are the NVIDIA H100 GPUs?
Impact of ARTEX AI on Crypto Companies
Amazon's MadPot honeypot recorded two campaigns between October 3 and November 5. The first hunted exposed AI applications such as LiteLLM and Dify to take model provider API keys, then used them to fund the search for the next keys.
The second targeted identity verification. According to Amazon Threat Intelligence, the agent built a real-time video deepfake pipeline with a single consumer graphics card and forged identity documents, allegedly for two crypto exchanges. The liveness vendor rejected every recorded deepfake attempt, while Amazon said it could not verify the results reported by the agent.
ChainGPT, via KuCoin News, added the Barracuda case. On November 1, attackers entered the company's cloud using an unrevoked AI vendor access key, then searched for Ethereum keystores, extended private keys, and seed phrases.
Barracuda stated that no wallet material was found, and emphasized that the tool does not necessarily indicate who the perpetrator was.
There is no evidence yet that ARTEX succeeded in draining crypto exchange funds. As for the perpetrators, Amazon only stated moderate confidence that its operators are a separate group linked to China.
Read Also: Aster Strengthens Wallet Security, ASTER Price Begins to Recover After a Decline
How to Counter AI Cyberattacks
According to AWS CISO CJ Moses, agents succeed when basic controls are absent: default credentials, keys left in code, unauthenticated interfaces, and unpatched software.
Amazon recommends replacing default administrator credentials, scanning CI/CD pipelines for embedded secrets, immediately rotating leaked keys, and monitoring spikes in AI service usage. The FBI asks organizations to reduce their attack surface and use zero-trust access.
SentinelOne assesses that IP blocking is increasingly less effective because agents move through residential proxies, so secret rotation, closing gaps, and EDR on every host are more important.
For ordinary users, enable two-factor authentication and do not store seed phrases in digital files.
Read Also: US Bank Outage 2026: JPMorgan Chase Bug Disrupts Other Banks' Transactions
Bittime Security: Registered and Supervised by OJK
Bittime is a Digital Financial Asset Trader (PAKD) registered and supervised by OJK. In a Bittime press release on October 6, 2026, security, mechanisms, and risk were cited as important parts of developing Spot, Staking, and Futures products.
The regulatory framework is also layered. POJK Number 23 of 2025 requires traders to separate consumers' digital financial assets from those of the trader, including in recording and bookkeeping. Its scope goes beyond storage, namely also balance reconciliation and asset ownership information.
Bittime Futures launched in July 2026 after obtaining a license from PT Central Finansial X (CFX) within the OJK supervision framework. Bittime's Operations Director, Ryan Lymn, assessed that security aspects will become increasingly important for building trust in the digital asset ecosystem.
Crypto trading remains risky. In Futures, leverage can magnify profits as well as losses and trigger liquidation, so understand the product before trading.
Conclusion
The series of ARTEX cyberattacks shows that AI automation shortens the distance between an exposed gap and an attack. There is no evidence yet of crypto exchange fund losses, but credential remediation cannot wait. Therefore, choosing a supervised platform and maintaining the security of your own account are both important.
FAQ
1. What is ARTEX AI?
An AI-agent-based penetration testing framework designed to test systems with the owner's authorization. The tool is now also used by criminals and groups suspected of being state-linked.
2. How fast can ARTEX breach a system?
The FBI recorded that some intrusions reached privileged access in less than three hours. SentinelOne mentions one suspected ARTEX case that went from a leaked GitHub secret to Azure Key Vault data in five minutes.
3. Is this ARTEX hacking tool illegal?
The tool was created for legitimate testing. Use without the system owner's permission is what violates the law. SentinelOne reminds that authorized testers also run ARTEX, so finding the tool alone does not prove an attack.
4. Is Bittime safe for crypto transactions?
Bittime is registered as a PAKD and supervised by OJK, and is required to separate consumer assets under POJK Number 23 of 2025. Still enable two-factor authentication and understand product risks before trading.
Disclaimer: The views expressed belong exclusively to the author and do not reflect the views of this platform. This platform and its affiliates disclaim any responsibility for the accuracy or suitability of the information provided. It is for informational purposes only and not intended as financial or investment advice.
.png)