Ledger Hardware Wallet Allegedly Modified, Crypto Users Need to Be Vigilant
2026-10-30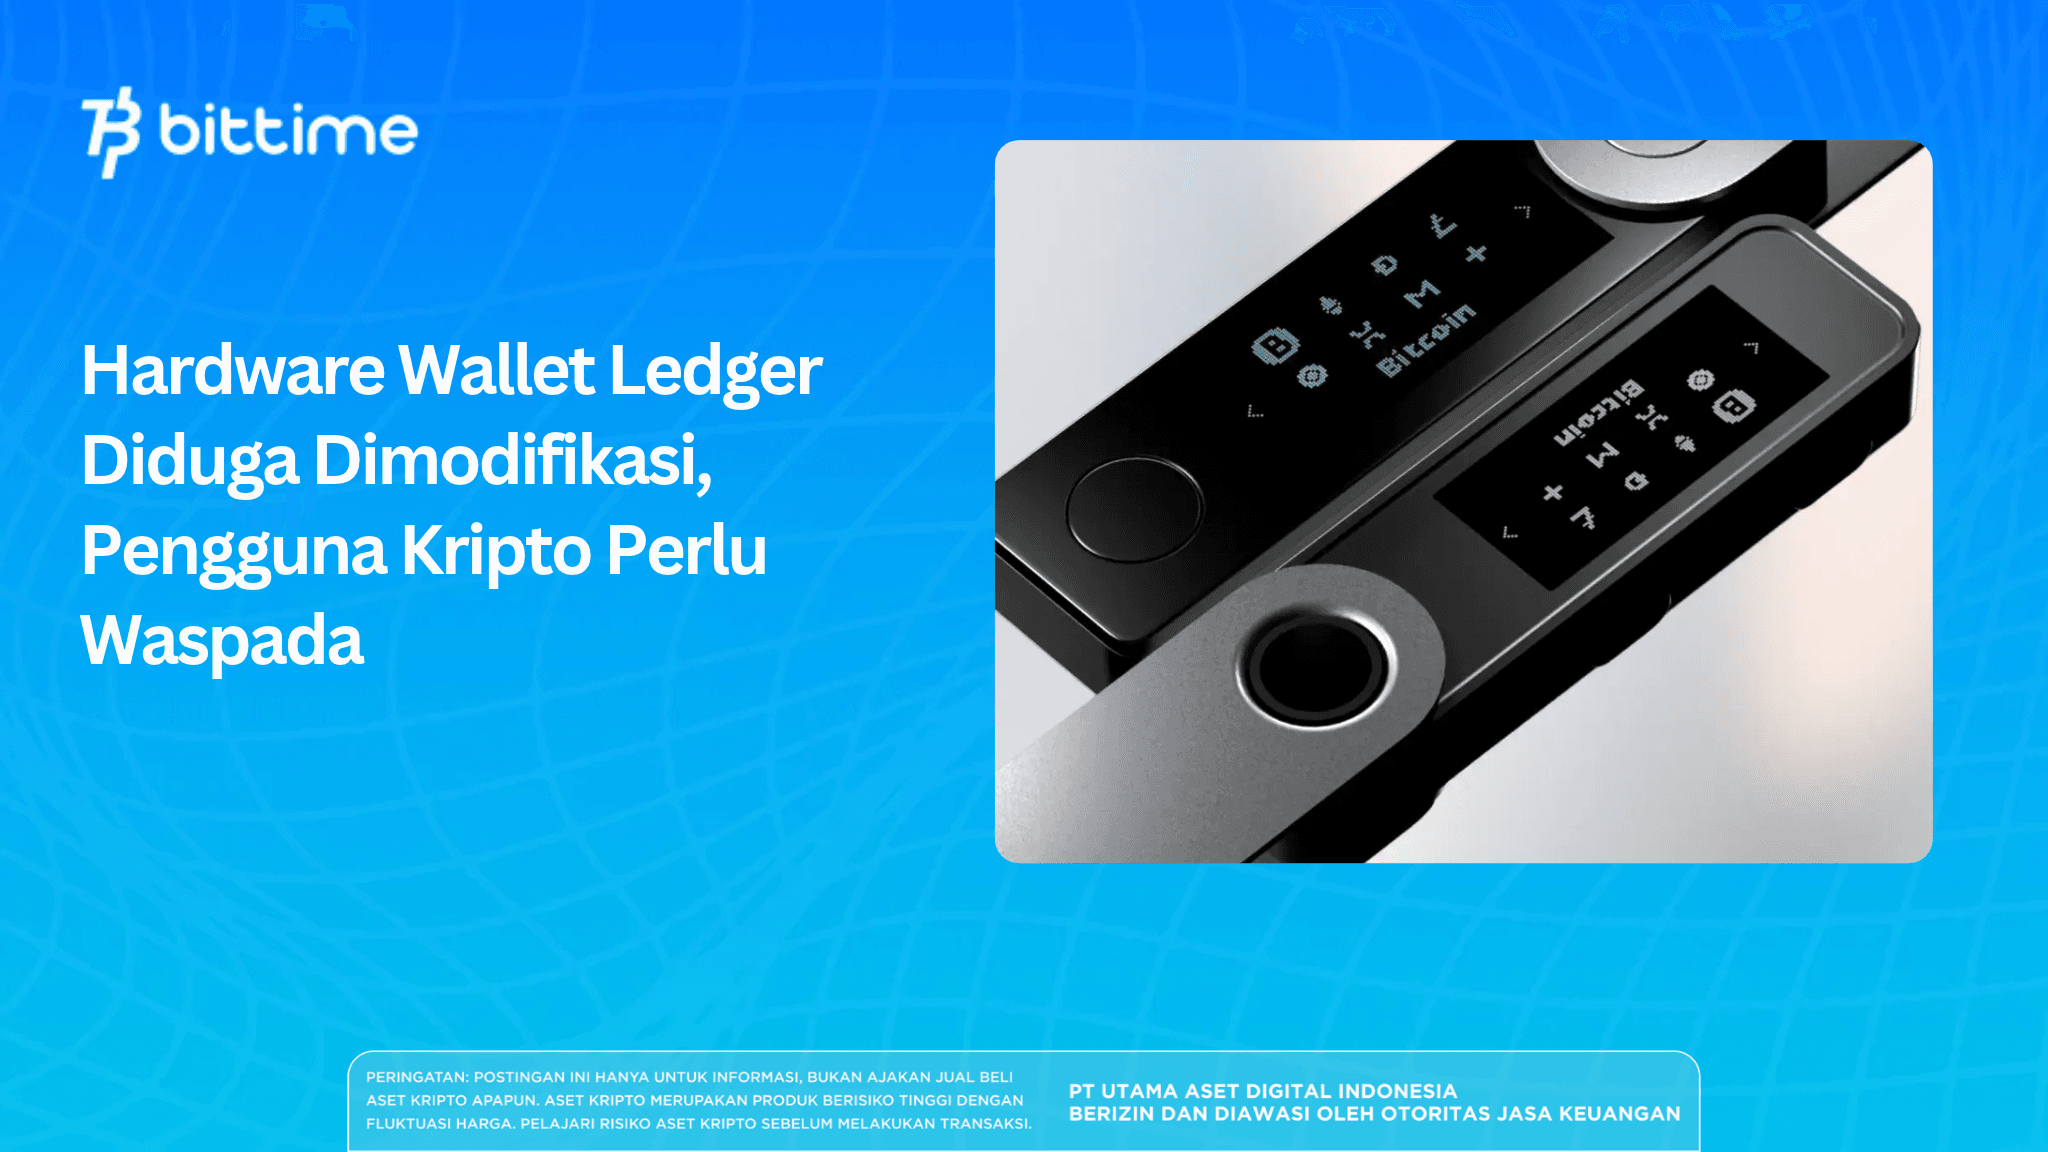
Two reports of asset losses totaling about SGD 3.5 million prompted the Singapore Police Force (SPF) to issue a warning on October 28, 2026.
Initial investigation results indicate that Ledger hardware wallets purchased at some retail stores in Singapore contained malicious hardware, namely dangerous components that cause the seed phrase to be stolen without the owner realizing it.
Key Takeaways
- SPF recorded at least two cases since September 10, 2026, with losses of about SGD 3.5 million.
- Malicious components in the device can capture the recovery phrase or private key, so assets can be moved without the owner's permission.
- Ledger says its chip, operating system, and servers were not compromised. The problem is in the distribution channel.
SPF Warning About Ledger Hardware Wallets from Retail Stores
In its official release, SPF said there had been at least two cases since September 10, 2026. The loss value was about SGD 3.5 million, equivalent to roughly USD 2.7 million based on the conversion by Unchained.
The initial investigation found components inside the devices capable of capturing the recovery phrase or private key. With that data, unauthorized parties could access victims' wallets and move their assets.
SPF has contacted Ledger, which is now reviewing the case. The police investigation is still ongoing. SPF's release did not name the store or device model, so it is not yet clear which units are affected.
The SGD 3.5 million figure also covers only cases reported in Singapore. Users who want to transact through a registered platform supervised by OJK can register at Bittime, a Digital Financial Asset Trader (PAKD) that provides Spot, Staking, and Futures trading.
How the Ledger Hardware Implant Works
Ledger explained that an organized criminal group bought genuine devices over several months. They installed hidden components, then resold them through resellers in Southeast Asia, according to Bankless. The components were designed to steal the 24-word recovery phrase when users set up the device.
According to CoinDesk, the implant sent wallet keys over a cellular network. Findings by Ledger researchers reported by Unchained point to something similar: an additional component read the recovery phrase when it appeared on screen, then sent it over LTE.
A report by Investing.com said an examination of a Ledger Flex purchased at Changi Airport found a modified display connector, a cellular chip, and a SIM card.
Ledger emphasized that its chip, operating system, and servers were not compromised. The company called this case a local distribution attack, not a systemic supply chain attack. Nevertheless, for device owners, a compromised Ledger wallet still means the seed phrase could leak from the setup process.
Read Also:
- Alleged Binance Hack: US$5.7 Billion in Crypto Assets Moved Becomes Spotlight
- Bittime Highlights Platform Legality and Consumer Protection
Connection to the CryptoBilis Case and Sales in Indonesia
Ledger began investigating theft reports on October 9, 2026. The case was initially linked to CryptoBilis, an official reseller operating in Malaysia, Indonesia, and the Philippines, according to KuCoin.
On October 13, Ledger asked resellers and distributors in Indonesia, Singapore, Thailand, the Philippines, Vietnam, Malaysia, and Hong Kong to stop sales and pull stock from shelves.
The scale of regional losses remains unclear. On-chain researchers estimate losses of up to USD 93 million across more than 300 wallets, but Ledger has not confirmed that figure, according to Bankless. Other media estimates range from USD 86 million to USD 102 million.
SPF did not explain whether the two Singapore cases are related to the CryptoBilis cluster. On the other hand, Ledger said device samples examined from stores and warehouses in Germany were clean.
The company is also preparing new reseller rules, including an obligation to report suspicious products and a ban on reselling returned devices.
Safe Steps for Hardware Wallet Owners
Regarding hardware wallet security, SPF gave three advisories:
- Monitor official information. Follow advisories from each wallet provider.
- Stop using suspected devices. Do not enter the recovery phrase or transact through that device. If you suspect the key has already leaked, move the remaining assets to a new wallet with a new recovery phrase created on a secure device, then contact the provider through official support channels.
- Do not share the seed phrase. This applies to anyone, including parties claiming to represent the wallet provider, an exchange, or law enforcement.
A basic understanding of crypto asset security, from platform legality to account security, still needs attention before deciding where to store assets.
Conclusion
The SPF warning shows that even devices designed to protect assets can become a vulnerability if modified before reaching the buyer. The investigation is still ongoing and there are no details yet on the store, model, or connection to the regional case.
Until there is certainty, users need to follow official advisories and treat the seed phrase as data that must not be shared with anyone.
Check the price of Bitcoin (BTC), Ethereum (ETH), XRP, Solana (SOL), GRAM, and BNB as well as leading memecoins DOGE. You can trade directly on Bittime!
Bittime is a licensed Digital Financial Asset Trader (PAKD) platform supervised by the Financial Services Authority — where you can buy Bitcoin in Indonesia and hundreds of other crypto assets starting from Rp10,000. The registration process is fast, secure, and can be started today.
Monitor USDT to IDR conversions and your favorite crypto asset price movements in real time. Everything is available in one crypto investment app that can be downloaded for free on the Play Store.
Ready to start? Register now on Bittime and execute your investment strategy with a platform trusted by millions of users in Indonesia.
FAQ
Are all Ledger devices sold in Singapore affected?
There is no data yet stating that. SPF only mentioned some devices from several retail stores. Ledger added that samples from stores and warehouses in Germany that were examined were declared clean.
Are buyers in Indonesia also affected?
Indonesia is among the seven regions where Ledger requested sales to be stopped on October 13, 2026. The sources cited in this article do not yet include details of victims per country.
Is the SGD 3.5 million loss the same as the USD 93 million estimate?
No. The SGD 3.5 million figure covers only two cases reported to SPF. The USD 93 million estimate comes from on-chain researchers for the regional scale and has not been confirmed by Ledger.
How can I buy a hardware wallet more safely?
Buy directly from the manufacturer's official store or an appointed reseller, and check the packaging condition. Be wary of devices that appear used or come with a recovery phrase already written down. This practice is common in hardware wallet security, not a finding specific to this case.
Disclaimer: The views expressed belong exclusively to the author and do not reflect the views of this platform. This platform and its affiliates disclaim any responsibility for the accuracy or suitability of the information provided. It is for informational purposes only and not intended as financial or investment advice.
.png)